
Understanding and Managing Abnormal Login Detection in SpinOne

This article explains what the Abnormal Login Detection (Default) policy detects, how to review its settings, how to investigate an alert, and how to reduce false alarms.
What the Policy Detects
Abnormal Login Detection is a default Activity Policy recommended by SpinOne. It alerts you when a user has repeated unsuccessful login attempts in a short period of time (for example, 3 failed attempts within 5 minutes). This can be a sign that someone is trying to guess a user’s password, also known as a brute force attack.
SpinOne gets this login activity directly from Google Workspace (or Microsoft 365). An alert doesn’t confirm that an account has been compromised; it’s a signal that the activity should be reviewed.
Review the Policy
Log in to your SpinOne account. From the left navigation panel, head to Security Policies > Policies Management and open Abnormal Login Detection (Default).
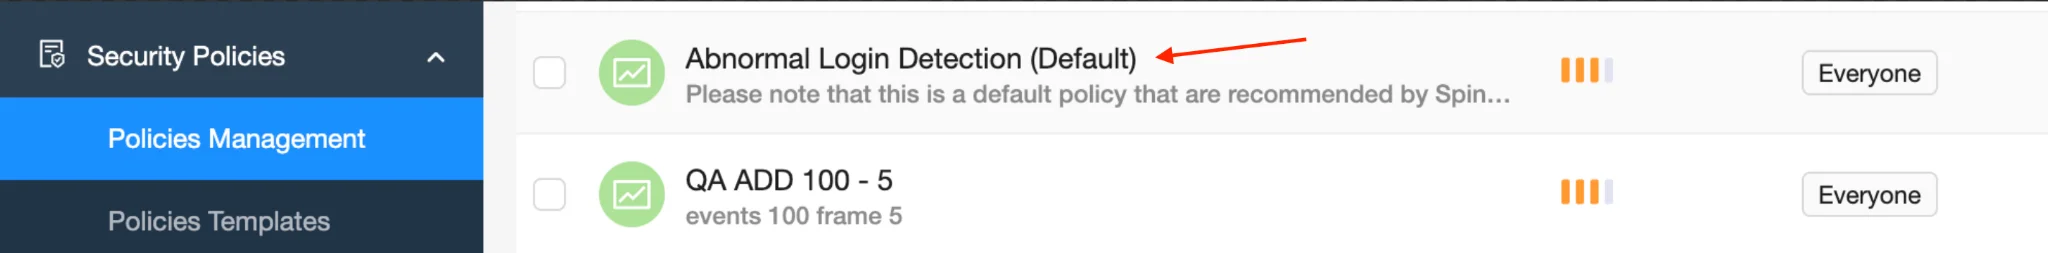
From here, you can adjust the policy to fit your organization:
- Act On: change how many failed attempts, and within what timeframe, trigger the policy.
- Action: add Send Notification to be alerted each time the policy triggers, add any additional action based on the organizations needs.
- Scope & Exception: apply the policy to everyone, or only to specific users and groups.
Investigate an Alert
Before concluding that an account has been accessed by someone else, review the alert in context. Consider whether the failed attempts came from a known user, device, location, IP address, or automated tool.
- Incident details: head to Cloud Monitor > Incidents to see when the policy was triggered and for which user.
- Login history: head to Cloud Monitor > Activity Log, filter the activity type by Login, and set the source to the user.
- User Audit: review a summary of the user’s security activity, including successful and unsuccessful logins. Navigate to Security> Identities>Users
If the activity is unexpected, follow your organization’s incident response procedures.
Reduce False Alarms
Legitimate activity can sometimes look like repeated failed logins. Common causes include automated tools signing in with an administrator’s account, and cached sessions when users switch between accounts. To reduce these alerts:
- Allowlist trusted IP addresses. In the policy, add the IP addresses your users or automated tools log in from. Failed logins from those addresses will no longer trigger the policy.
- Use a dedicated service account for automated tools. Moving automated tools off an administrator’s personal account keeps their activity separate and easier to review.
After making these changes, keep an eye on new alerts to confirm the expected activity is no longer flagged. Your security monitoring for all other activity stays fully active.
If you have any questions or concerns, please contact us at support@spin.ai.
Get more information on Google Workspace™ Backup Solutions