Cyberhaven Fallout Widens with 8 More Compromised Extensions” Characters
- What Was the January 28 Update?
- What Is the Brief Overview of the Cyberhaven Incident?
- What Did Spin.AI’s Exclusive Findings Reveal?
- What Are Spin.AI’s Newly Discovered Compromised Extensions?
- What Are the Known Compromised Browser Extensions?
- What Are the Recommended Actions?
- Talk to Us
- Frequently Asked Questions
tl;dr executive summary:
Spin.AI’s own investigation reveals eight additional browser extensions compromised in the Cyberhaven attack, affecting 1.1 million more users beyond earlier estimates.
These findings expand the total impact to 40 compromised extensions and 3.7 million users, with evidence showing some extensions were infiltrated as early as 2023 and remained compromised for hundreds of days before patching.
The report urges individuals and organizations to verify extension versions, update or remove compromised tools, reset Facebook passwords, and enable MFA to mitigate risks from stolen cookies and ongoing threat activity.
Spin.AI’s latest research has uncovered 8 additional compromised browser extensions, used by 1.1 million users during the time of compromise. This discovery brings the total number of compromised extensions to 40, impacting 3.7 million users in total.
The fallout from the Cyberhaven cyberattack continues to escalate. New findings by Spin.AI reveal the scale of affected users targeted with compromised extensions is even larger than initially thought. The attack is now known to have compromised additional browser extensions, putting 3.7 million users at risk.

What Was the January 28 Update?
We processed our database with the remaining IOCs and did not find other extensions included as part of this attack campaign. We continue to monitor the six remaining compromised extensions still available on the marketplace for patches and will update the table in this post accordingly.
What Is the Brief Overview of the Cyberhaven Incident?
The Cyberhaven cybersecurity incident first became known when its extension developer fell victim to a phishing attempt and consequently, had malicious code injected into its Chrome extension. After investigation by Cyberhaven, Secure Annex, and others, it was uncovered that this attack is part of a broader campaign to target Chrome Extension developers.
What Did Spin.AI’s Exclusive Findings Reveal?
In response to the Cyberhaven attack, our team of security researchers conducted an extensive investigation into the malicious extension campaign. We processed our database with the Indicators of Compromise (IOCs) published by others and noted the following findings:
No Spin.AI Customers Affected By Phishing Attempt
We reviewed the OAuth ID used in the phishing attempt and found no evidence of our customers falling victim to this phishing attempt.
8 Compromised Extensions Not Previously Reported
We processed our database using the IOCs and found the sclpfybn[.]com domain in 8 extensions that were not previously reported. These 8 extensions were used by 1.1 million users during the time of compromise.
Signs of This Attack Campaign Starting in 2023
Thanks to our database, which maintains a history of all browser extensions, we found that the earliest the sclpfybn[.]com domain was detected was in September 2023. While many browser extensions were either quickly patched or removed from the Chrome Web Store, some browser extensions were compromised for over 300 days before receiving a patch.
One Extension Was Compromised Earlier Than Initially Reported
One extension (AI Shop Buddy/Amazon Search; epikoohpebngmakjinphfiagogjcnddm) was previously reported to be compromised in v2.7.3. Our database indicates the compromise really began in v2.7.0.

What Are Spin.AI’s Newly Discovered Compromised Extensions?
Our internal investigation uncovered an additional eight compromised extensions. These additional extensions affected approximately 1.1 million new users in addition to the original 2.6 million. The findings highlight the growing reach of the Cyberhaven attack. Below are the names and details of these newly identified extensions:
| Extension Name | ID | Compromised Version | Date of Compromise | Patched Version | Date of Patch |
| Hub VPN – Free VPN Proxy | lneaocagcijjdpkcabeanfpdbmapcjjg | 1.1.7 | 5/26/2024 | 1.1.8 | 6/6/2024 |
| BitTorrent | aahnibhpidkdaeaplfdogejgoajkjgob | 13.1.0.4, 13.1.0.5, 13.1.0.6 | 3/30/2024 | 13.1.0.7 | 7/15/2024 |
| BrowserSpy | cenplbjdopjciamjdjiehflkhfjmklhm | 0.8, 0.9, 0.10, 0.12, 0.13 | 9/10/2023 | N/A – Removed from marketplace | N/A – Removed from marketplace |
| GPT Login | didhgeamncokiaegffipckhhcpnmlcbl | 1.1.3 – 1.3.1 | 2/19/2024 | N/A – Removed from marketplace | N/A – Removed from marketplace |
| ChatGPT Plus – AI chatbot for Google | egokoghkkmcnnemgcaadjhdihpceopkn | 1.2.9, 1.3.0 | 12/12/2023 | N/A – Removed from marketplace | N/A – Removed from marketplace |
| Chat GPT | fnmihdojmnkclgjpcoonokmkhjpjechg | 1.5.8 – 1.6.5 | 12/25/2023 | 1.7.0 | 4/2/2024 |
| Web Mark: bookmark/history/clipboard bundler | jdleicahfbehiikjcaocollfhbnigplo | 3.4, 3.5 | 10/22/2023 | 3.7 | 8/25/2024 |
| Copy and Paste more | mjijaapcbpbcppapekipkdhipfcdpidb | 4.1 | 12/16/2023 | 4.3 | 8/25/2024 |
What Are the Known Compromised Browser Extensions?
The table below details the extensions that were first identified as compromised, along with affected versions, date of compromise, current patch status, and date of patch (if applicable). The total number of users from the initially known compromised extensions totaled 2.6 million.
| Extension Name | ID | Compromised Versions | Date of Compromise | Patched Version | Date of Patch |
| VPNCity | nnpnnpemnckcfdebeekibpiijlicmpom | 2.0.1 | 12/11/2024 | 2.2.2 | 1/23/2025 |
| Parrot Talks | kkodiihpgodmdankclfibbiphjkfdenh | 1.16.2 | 12/24/2024 | 1.16.3 | 12/29/2024 |
| Uvoice | oaikpkmjciadfpddlpjjdapglcihgdle | 1.0.12 | 12/25/2024 | 1.0.13 | 12/30/2024 |
| Internxt VPN | dpggmcodlahmljkhlmpgpdcffdaoccni | 1.1.1 | 12/24/2024 | 1.1.2 | 12/26/2024 |
| Bookmark Favicon Changer | acmfnomgphggonodopogfbmkneepfgnh | 4.00 | 12/24/2024 | 5.1 | 12/29/2024 |
| Castorus | mnhffkhmpnefgklngfmlndmkimimbphc | 4.40 | 12/25/2024 | 4.41 | 12/26/2024 |
| Wayin AI | cedgndijpacnfbdggppddacngjfdkaca | 0.0.11 | 12/18/2024 | 0.0.12 | 1/17/2025 |
| Search Copilot AI Assistant for Chrome | bbdnohkpnbkdkmnkddobeafboooinpla | 1.0.1 | 7/16/2024 | N/A – Removed from marketplace | N/A – Removed from marketplace |
| VidHelper – Video Downloader | egmennebgadmncfjafcemlecimkepcle | 2.2.7 | 12/24/2024 | 2.2.9 | 1/27/2025 |
| AI Assistant – ChatGPT and Gemini for Chrome | bibjgkidgpfbblifamdlkdlhgihmfohh | 0.1.3 | 5/30/2024 | N/A – Removed from marketplace | N/A – Removed from marketplace |
| TinaMind – The GPT-4o-powered AI Assistant! | befflofjcniongenjmbkgkoljhgliihe | 2.13.0, 2.13.1 | 12/14/2024 | 2.14.0 | 12/20/2024 |
| Bard AI chat | pkgciiiancapdlpcbppfkmeaieppikkk | 1.3.7 | 9/4/2024 | N/A – Removed from marketplace | N/A – Removed from marketplace |
| Reader Mode | llimhhconnjiflfimocjggfjdlmlhblm | 1.5.7, 1.5.8 | 12/7/2024 | 1.6.2 | 1/4/2025 |
| Primus (prev. PADO) | oeiomhmbaapihbilkfkhmlajkeegnjhe | 0.3.18, 0.3.19 | 12/17/2024 | 0.3.20 | 12/24/2024 |
| Tackker – online keylogger tool | ekpkdmohpdnebfedjjfklhpefgpgaaji | 1.3 | 10/5/2023 | 1.4 | 8/12/2024 |
| AI Shop Buddy | epikoohpebngmakjinphfiagogjcnddm | 2.7.0, 2.7.1, 2.7.2, 2.7.3, 2.7.5, 2.7.6 | 10/31/2023 | Not patched yet | Not patched yet |
| Sort by Oldest | miglaibdlgminlepgeifekifakochlka | 1.4.5 | 1/10/2024 | N/A – Removed from marketplace | N/A – Removed from marketplace |
| Rewards Search Automator | eanofdhdfbcalhflpbdipkjjkoimeeod | 1.5.0 | 8/25/2024 | Not patched yet | Not patched yet |
| Earny – Up to 20% Cash Back | ogbhbgkiojdollpjbhbamafmedkeockb | 1.8.1 | 4/4/2023 | N/A – Removed from marketplace | N/A – Removed from marketplace |
| ChatGPT Assistant – Smart Search | bgejafhieobnfpjlpcjjggoboebonfcg | 1.1.1 | 2/11/2024 | N/A – Removed from marketplace | N/A – Removed from marketplace |
| Keyboard History Recorder | igbodamhgjohafcenbcljfegbipdfjpk | 2.3 | 7/28/2024 | 2.5 | 2/8/2025 |
| Email Hunter | mbindhfolmpijhodmgkloeeppmkhpmhc | 1.44 | 9/16/2024 | N/A – Removed from marketplace | N/A – Removed from marketplace |
| Visual Effects for Google Meet | hodiladlefdpcbemnbbcpclbmknkiaem | 3.1.3, 3.1.4, 3.1.7, 3.2.3 | 6/12/2023 | 3.2.4 | 1/9/2024 |
| Cyberhaven security extension V3 | pajkjnmeojmbapicmbpliphjmcekeaac | 24.10.4 | 12/24/2024 | 24.10.5 | 12/24/2024 |
| GraphQL Network Inspector | ndlbedplllcgconngcnfmkadhokfaaln | 2.22.6 | 12/29/2024 | 2.22.7 | 12/29/2024 |
| GPT 4 Summary with OpenAI | epdjhgbipjpbbhoccdeipghoihibnfja | 1.4 | 8/10/2024 | N/A – Removed from marketplace | N/A – Removed from marketplace |
| Vidnoz Flex – Video recorder & Video share | cplhlgabfijoiabgkigdafklbhhdkahj | 1.0.161 | 12/23/2024 | 1.0.165 | 1/4/2025 |
| YesCaptcha assistant | jiofmdifioeejeilfkpegipdjiopiekl | 1.1.61 | 12/29/2024 | 1.1.62 | 1/2/2025 |
| Proxy SwitchyOmega (V3) | hihblcmlaaademjlakdpicchbjnnnkbo | 3.0.2 | 12/28/2024 | 3.0.3 | 1/7/2025 |
| ChatGPT App | lbneaaedflankmgmfbmaplggbmjjmbae | 1.3.8, 1.3.9, 1.4.0, 1.4.1, 1.4.2 | 9/2/2024 | Not patched yet | Not patched yet |
| Web Mirror | eaijffijbobmnonfhilihbejadplhddo | 2.4 | 11/12/2023 | Not patched yet | Not patched yet |
| Hi AI | hmiaoahjllhfgebflooeeefeiafpkfde | 1.0.0 | 7/28/2024 | N/A – Removed from marketplace | N/A – Removed from marketplace |
What Are the Recommended Actions?
Whether it be individuals who may have downloaded or updated to one of the compromised extensions or organizations who may be impacted in a larger way, there are key takeaways and action items to be aware of.
Individual users and businesses are encouraged to take the following steps as soon as possible:
Verify Whether the Extension Was Used During the Period it Was Compromised
Take an inventory of the browser extensions and its version. If the compromised version was/is installed, uninstall or update them immediately.
Change Facebook Password
The data exfiltration activities for this particular attack seemed to center around Facebook business accounts. It is important to make sure Facebook account passwords are reset to minimize the damage of potentially stolen cookies.
Enable Multi-Factor Authentication (MFA)
This additional security layer makes it much more difficult to compromise user accounts.
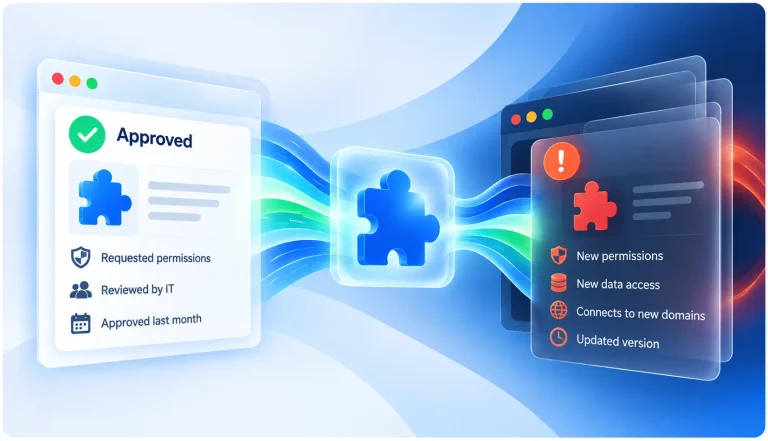
The Cyberhaven attack shows that while third-party browser extensions and SaaS apps can increase productivity, they can also pose a significant security threat. We are committed to helping users stay informed and secure by sharing our security research with the community. To learn more about how our solution can protect your organization from similar threats:
Talk to Us
Schedule a call with our security specialists to discuss your organization’s risk exposure and ways to mitigate it.
As this story develops, we will continue to provide updates and findings to help you safeguard data and users from new and emerging attacks.
Frequently Asked Questions
Yes, the compromised extensions were/are accessible on all Chromium-based browsers. Edge users who have installed these extensions may also be at risk. This blog provides a detailed list of additional compromised extensions, along with their affected versions and the dates of compromise or patching. You can use this information to verify whether you were using any of these extensions during the affected period.
Some extensions remained compromised for over 300 days before receiving a patch, showing how long attackers maintained access unnoticed .
Users should uninstall or update affected extensions, reset Facebook passwords, and enable MFA to reduce risk from stolen cookies and unauthorized access.